Updated my test mastodon instance to 4.5.9, no issues (so far).
mastoadmin
RE: https://mastodon.social/@MastodonEngineering/116810207094278507
Another security patch update!
All our instances have been upgraded to v4.6.2 without incident.
Have a great day y'all! 👋
[important] Sleeper account registrations on Fedi
Edited 11d ago

New release of Mastodon Bots (ActivityPub Mastodon-copmpatible bot instance that is probably the quickest to spin up a new Fediverse content bot under 20 seconds):
https://github.com/nekromoff/mastodon-bots
#mastoAdmin #masto #Mastodon #webdev #bot #bots #php #activityPub #apI #development
【站长提醒|大范围撞库盗号】
最近联邦宇宙出现一轮大规模撞库盗号:9 月 6 日 12:05–12:41 UTC 短短一小时内,至少 82 个实例、142+ 个账号被同一套脚本改名为「HACKED - Join t[.]me/HomeFucker5」并置顶垃圾帖。我站也有两个账号中招。
这是撞库(拿其他网站泄露的邮箱+密码来登录),不是 Mastodon 或站点的安全漏洞:从 4.1 到 4.8-nightly、已打满补丁的实例都被命中。攻击者先用密码悄悄"验号",几周后再集中变现,所以现在没发帖不代表没被盗。
建议各位站长排查:
• 登录记录(login_activities)中 UA 为 Go-http-client/1.1 的成功登录,尤其来自这三个 IP:193.202.84.104、45.134.142.231、81.92.219.205
• 昵称含「HACKED」的账号;近期新建的、名为「boost」的 OAuth 应用
• 命中的账号:重置密码、吊销全部会话与应用授权、通知本人
• 提前在 管理 → 审核 → IP 规则 把上述 IP 设为「禁止访问」
也请提醒所有用户:换一个只在本站使用的新密码,开启两步验证,密码不要和其他网站重复。
—————
[Admin alert | Mass credential-stuffing account takeovers]
A large credential-stuffing wave hit the fediverse on 6 Sep 2026, 12:05–12:41 UTC: 142+ accounts on 82+ instances were renamed "HACKED - Join t[.]me/HomeFucker5" with pinned spam. Two accounts on my instance were hit.
This is credential stuffing (leaked email+password pairs from other sites), NOT a Mastodon or server vulnerability: victims run everything from 4.1 to 4.8-nightly, including fully patched servers. The bot quietly validates passwords weeks in advance and monetizes in one wave, so "no spam yet" does not mean "not compromised".
Admins, please check:
• login_activities for successful logins with user-agent Go-http-client/1.1, especially from 193.202.84.104, 45.134.142.231, 81.92.219.205
• display names containing "HACKED"; recently created OAuth apps named "boost"
• For any hit: reset the password, revoke all sessions and app authorizations, notify the user
• Pre-emptively add those IPs under Moderation → IP rules as "No access"
Please remind your users: set a new password used only here, enable 2FA, and never reuse a password across sites.

We just released Mastodon 4.7.0!
This version contains very few user-facing changes, but significantly reworks the backend code to improve security and support new protocol features.
You can read more about it on our blog: https://blog.joinmastodon.org/2026/08/mastodon-4.7/
Note for admins: the database migrations might take a long time, this is expected (see the release notes).
Release notes and upgrade instructions are available here: https://github.com/mastodon/mastodon/releases/tag/v4.7.0
mastodon.social is currently undergoing a major Denial of Service (DDOS) incident. The team is working on this as a matter of priority. Thank you for your patience!
If you're running a public Mastodon server, it is really important to set aside running costs for three months. Leave this money in a separate account if possible, and do not touch it for as long as your server is running.
This three month set-aside means you can guarantee your members three months warning if you ever decide to close the server, which is plenty of time to move accounts. This gives your server credibility both with existing members and potential new members.
Edited 80d ago
@matt_birchler fork of @TangerineUI is now installed as an optional theme on Listodon. Yay!
We just released Mastodon 4.6.3, containing several bug fixes.
Full release notes and update instructions are available on the GitHub release page.
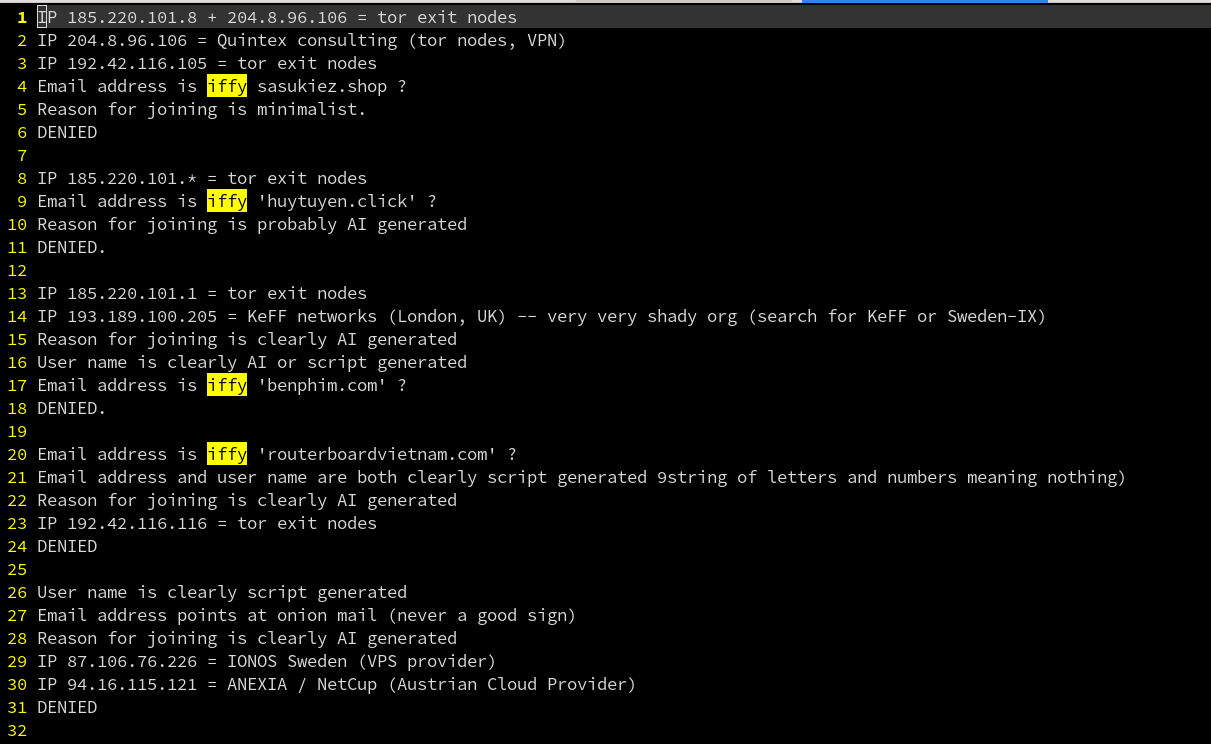
Vacations are finished and spammers and trolls are back to their usual tricks to try and open accounts on the Fediverse. Refused access to 8 accounts.
As a reminder, here are a few tips:
- Is the email legit?
- Is the email and user name meaningful? kwduifb is not meaningful.
- Do the IP addresses point to Tor exit nodes or shady hosting operations?
- Is the reason for joining meaningful or AI generated?
Separately, none of these are enough to refuse access, but together...
Edited 26d ago
📬 Trunk & Tidbits for June 2026 is now live!
Our monthly blog post series is there to showcase what we worked on last month.
In this edition, we are also discussing our official Helm Chart for Mastodon, for those of you who deploy Mastodon on Kubernetes. We released a brand new version of the chart in a new place, deprecating the existing one.
https://blog.joinmastodon.org/2026/07/trunk-tidbits-june-2026/
We've closed signups on indieweb.social for the weekend after a huge increase in attempted spam sign ups.
We aren't the only instance going through this. Please show your support to the amazing moderators across the Fediverse! 💙 ☁️
#FediAdmin #SpamWave #Moderation #Admin #Indieweb #FediMod #MastoAdmin
Listodon has been updated to #Mastodon v4.7.1
No issues, tho my routine notes have me doing a bundle install, yarn install --immutable, and RAILS_ENV=production bundle exec rails assets:precompile on every upgrade.
It seems that this simply required a bundle install this time...it seemed to work just fine, at least I see the updated version number when restarted.

There will be some downtime of chaos.social due to maintenance starting in the next few minutes. #mastoadmin
➡️ https://about.iftas.org/2026/09/11/boom-protocol-spam/
the page linked above will re-post tips, tricks, guidance to combat the #bpSpam wave impacting many service providers.
#BoomProtocol #BoomProtocolProbe #Spam #FediAdmin #MastoAdmin #PeerTubeAdmin #FediMods #Mastomods
Edited 6d ago
We just released Mastodon v4.7.2, v4.6.8, v4.5.18 and v4.4.25.
In addition to several bugfixes, they disable HEIF processing to avoid a known critical security issues. We encourage server administrators to update as soon as possible.
Full release notes and update instructions are available on the GitHub releases page.

Quick heads-up for other Mastodon admins: this registration spam wave isn't over yet.
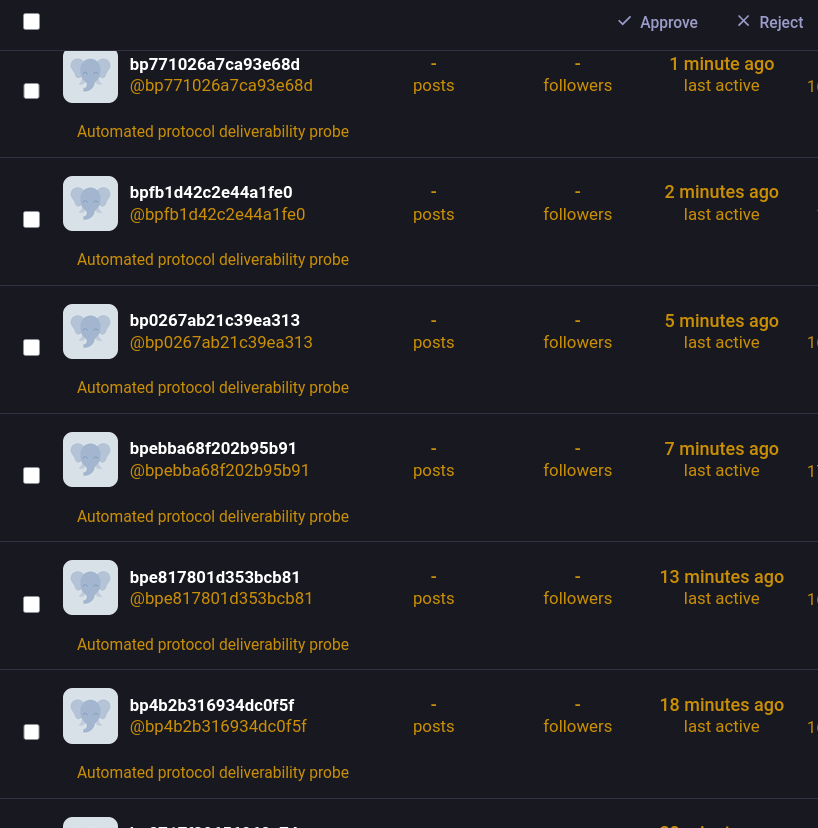
On lsbt.me, we first saw a flood of API registrations using Python/aiohttp. The telltale signs were usernames following the pattern bp plus 16 hex characters, and the sign-up reason was always "Automated protocol deliverability probe". A narrow block on that user agent stopped the first wave.
Today, however, five new registrations came in with the same usernames and the same sign-up reason. This time the bot simply identified itself as Chrome 126. That's exactly why a user agent is only useful as a short-term filter. It's a header the client can set to anything.
The requests go to POST /api/v1/accounts. This endpoint lets client apps create a new local account directly in the app. No app needs it for OAuth connections to existing accounts. #FediSuite doesn't use it either. It registers itself via /api/v1/apps, obtains consent via /oauth/authorize, and then works with a user token. Regular sign-up through the Mastodon website is also handled separately via POST /auth.
So I've completely disabled API account creation on lsbt.me. Web sign-up, OAuth, and existing clients keep working as before. Anyone who wants a new account just signs up once on the web as usual and can then use any client.
If you'd also rather not offer this optional native sign-up path, you can add the following to your Nginx server block, before the general location / block. The example assumes the @proxy location that many Mastodon Nginx configs already include:
location = /api/v1/accounts {
limit_except GET {
deny all;
}
try_files $uri @proxy;
}
This returns a 403 only for POST /api/v1/accounts. The read-only GET endpoint remains reachable. As always, run nginx -t afterwards and only reload once the test passes.
#Mastodon #Fediverse #MastoAdmin #FediAdmin #FediMod #FediBlock #Moderation #Registration #Spam #Nginx #SelfHosting #SysAdmin #ActivityPub
Mastodon updated to v4.7.2, a critical security update. Is anyone else surprised that you don't have to run the bundle / yarn / RAILS_ENV steps in the last few patches? A happy surprise for me!
Is there a way to block registrations from any e-mail that has a subdomain in it? #AskFedi #MastoAdmin