PSA for people with #Wordpress blogs: do you know that you can turn off comments on old posts?
In the last few months I have noticed a significant uptick in spammy comments on my Wordpress blogs (I have 4).
Well there is a way to remedy all that: you can simply turn off comments on old blog posts by going to:
Settings -> Discussion -> and checking "Automatically close comments on old posts"
(You can even determine the "oldness" of posts, for example, older than 7 days, 14 days... anything you'd like)
Enabling this made all the difference for me. I could not recommend it more.
End of my PSA 🤗
Have a great day everyone!
#blog #blogging #selfhosting #spam
spam

#PSA
#Mastodon, nor the #Fediverse in general will never ask you to "verify" with payment details, especially not from a non-moderator account. If you get a message asking you to verify, it is a #Scam #Bot, and you should block and #report it to #moderation.
We are currently getting a wave of #spam from bots like this. Again, do not even click the link, just block and report.
- TechHub Moderation
![Stop: Verification Required
Hello!
We have temporarily restricted your
Mastadon account. You must verify your
identity to remove all restrictions and
continue using Mastadon. We ask that you
confirm your bank details within 24 hours.
Once the verification is complete, all
restrictions will be removed and your
Mastadon account will be active again. We
thank you for your patience and
understanding.
Step 1
Method Verity
OM VISA o@ oe (© Jue]
@ Acceptrules Terms of Use and
Policies](/proxy/post_attachment/128810/12fe23848f.png "Stop: Verification Required
Hello!
We have temporarily restricted your
Mastadon account. You must verify your
identity to remove all restrictions and
continue using Mastadon. We ask that you
confirm your bank details within 24 hours.
Once the verification is complete, all
restrictions will be removed and your
Mastadon account will be active again. We
thank you for your patience and
understanding.
Step 1
Method Verity
OM VISA o@ oe (© Jue]
@ Acceptrules Terms of Use and
Policies")

Edited 1y ago

Please note: Until Mastodon's bugged notification filters are fixed, I redirect all mentions to /dev/null.
Sorry for the inconvenience, but I can not tolerate the current amount of #SPAM.
Edited 1y ago
Codeberg: Spam and DoS attacks on non-commercial development platform
Masses of spam messages, overflowing email inboxes and clogged internet lines: Anonymous attacks plague the non-profit Github alternative.
#Cybercrime #DoSSchwachstelle #Git #GitHub #OpenSource #Softwareentwicklung #Spam #news

I am using Google Classroom, and Gmail is marking all email notifications from my Google classroom as spam. It's email generated by one Google product going into another Google product. What on earth is happening to flag the notification as spam?
#Google #GoogleClassroom #Gmail #spam #MonopolistsDontInnovate
This post is not an invitation to scold me for using Google products or to suggest alternatives. It is also not a request for technical support.
#Google #GoogleClassroom #Gmail #spam #MonopolistsDontInnovate
This post is not an invitation to scold me for using Google products or to suggest alternatives. It is also not a request for technical support.

Got spam emails this morning by someone who opened an issue on GitHub with what was probably a very unsafe link and then just tagged dozens of users over and over and over. Why we needed 50 copies in a row of the same notification, IDK. Thankfully, the account is terminated already, but if this starts to be a regular thing, I might have to abandon GitHub altogether.
If you get a DM saying "call me the Fediverse chick", it's a spam. Don't click the links, but DO report it!
Reports from users are really important, especially if they are about spam DMs because no one else can see the spam except the user.
You can report posts by clicking ⋯ on the post and selecting "Report". When you report it, make sure to select the option to forward the report to the server it came from so that the admin there can delete the spammer's account.
Edited 1y ago


Since November 28th of this year I've received 22 spam emails with the same title "Let's start getting to know each other." (with the period at the end) from senders with names like Ellie, Emily, Harper, Olivia, and Aria. I haven't been able to find information about an ongoing scam like this. Has anyone else been seeing this one?
(I'm not asking for advice about dealing with spam. SpamAssassin has this one well in hand. I'm just curious if anyone else has been seeing spam like this).
#spam #email #AskFedi
(I'm not asking for advice about dealing with spam. SpamAssassin has this one well in hand. I'm just curious if anyone else has been seeing spam like this).
#spam #email #AskFedi
告知:垃圾消息攻击
最近有人在滥用开放注册的实例发送垃圾消息,来给一个游艇交易网站打广告。
你可以使用站内搜索功能搜索yachttrading并拉黑绝大多数帐号,管理员可以进一步封禁本站的帐号。垃圾消息通常包含一小段文字和一个到游艇交易网站的链接,文字使用的语言不定,但都非常生硬地试图把回复帖子的主题转到游艇上。
#垃圾消息 #什么值得B #Spam
已经发现的垃圾消息帐号:
https://dvd.chat/@lijh
https://dvd.chat/@jonnyking11
https://dvd.chat/@kew11
https://dvd.chat/@keke
https://dvd.chat/@kliu
https://dvd.chat/@winnie11
https://dvd.chat/@xiaoli
https://dvd.chat/@likeke
https://dvd.chat/@lidada
Edited 1y ago
My spam folder has taken on a special, highly-focused quality.
I'm not sure how Layla and May001 snuck past SpamAssassin but the assassin is being re-trained.
#spam #JunkMail #SpamAssassin #email
I'm not sure how Layla and May001 snuck past SpamAssassin but the assassin is being re-trained.
#spam #JunkMail #SpamAssassin #email

Edited 268d ago

Marre des appels indésirables ? Un développeur français vous propose de bloquer plus de 16 millions de numéros sur iOS et Android.
https://framablog.org/2025/09/23/sarah-qui-ca-raccroche/
#spam #ios #android

This is a long time coming. I've been posting about the decline of arXiv's CS category for a long time now, and even had a few conversations with someone I know who works there about it. Personally, I think the slop started in 2018--prior to generative AI slop--when the CS category at arXiv began the unsustainable exponential growth in submissions that has continued till today. An increasing number of what amounted to corporate whitepapers and other marketing materials were being posted on arXiv to give them the appearance of scientific credibility. There was a fairly clear arXiv-to-Nature pipeline. Citation counts were pumped as some of the scientometric services count arXiv "articles" as citations, and some researchers adopted the bad scholarly habit of citing arXiv preprints instead of the final publication. It was and still is a mess. My understanding is that arXiv was meant as a place for people to put high-quality but pre-publication articles, but at least in the CS category it's drifted quite far from that.
I gather they've finally taken this measure because of the preponderance AI-generated slop, but with any luck these other issues will improve too. The arXiv press release states “Review/survey articles or position papers submitted to arXiv without this documentation will be likely to be rejected and not appear on arXiv” so it does sound like they are acknowledging the other problems and intend to enforce their rules more strictly in the future.
"arXiv says it will no longer accept Computer Science papers that are still under review due to the wave of AI-generated ones it has received."
From https://infosec.exchange/users/josephcox/statuses/115486903712973154
#arXiv #preprint #CS #spam #AISlop #AI #GenAI #GenerativeAI
I gather they've finally taken this measure because of the preponderance AI-generated slop, but with any luck these other issues will improve too. The arXiv press release states “Review/survey articles or position papers submitted to arXiv without this documentation will be likely to be rejected and not appear on arXiv” so it does sound like they are acknowledging the other problems and intend to enforce their rules more strictly in the future.
"arXiv says it will no longer accept Computer Science papers that are still under review due to the wave of AI-generated ones it has received."
From https://infosec.exchange/users/josephcox/statuses/115486903712973154
#arXiv #preprint #CS #spam #AISlop #AI #GenAI #GenerativeAI
Edited 316d ago
The companies that redirect me to their home page after I unsubscribe from their mailing list mystify me. Obviously I do not want to have you in my life any more so what are you even doing?
#spam
#spam
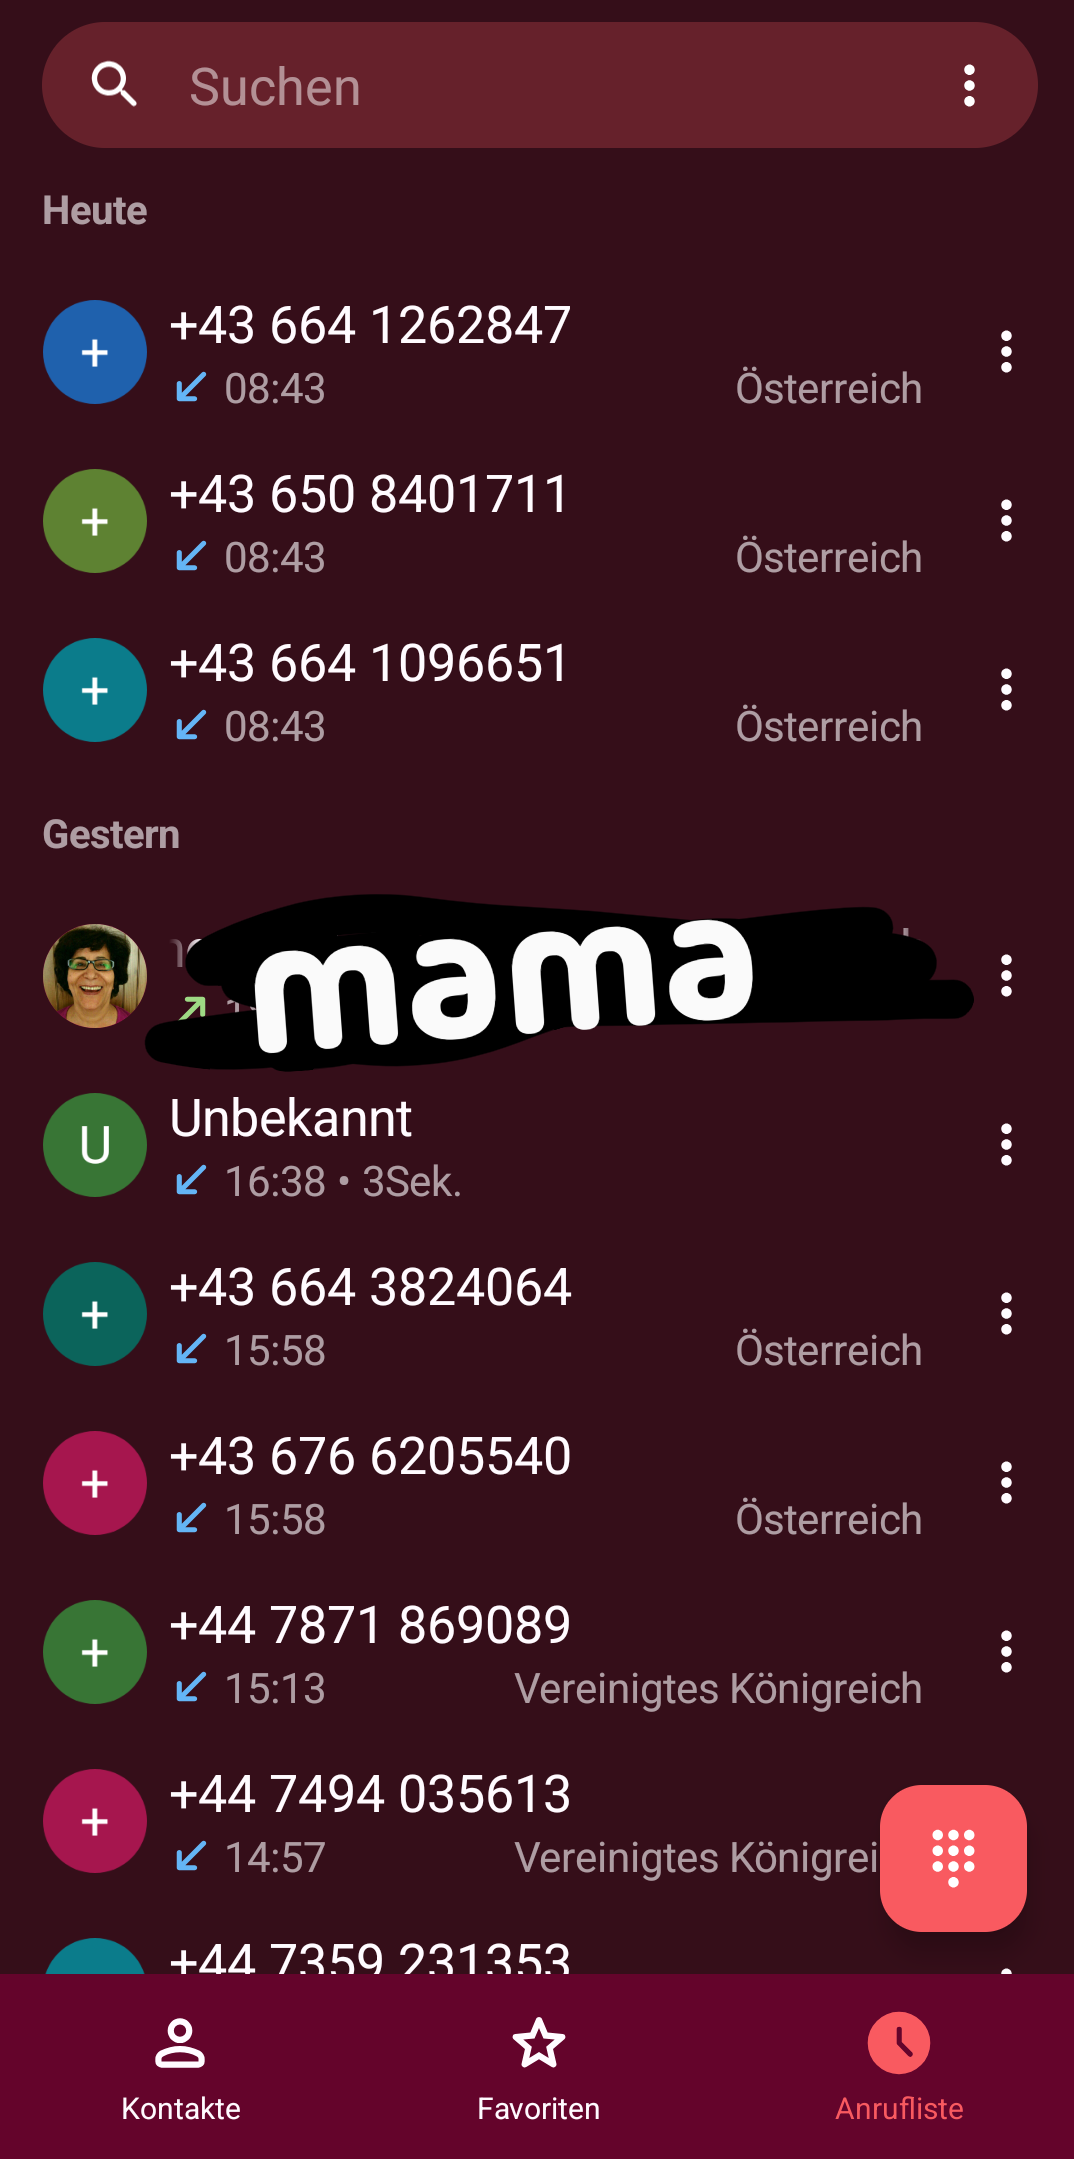
Wegen extremer Spam-Anrufe muss ich alle Anrufe blockieren, die von Unbekannt oder mir unbekannten Nummern kommen.

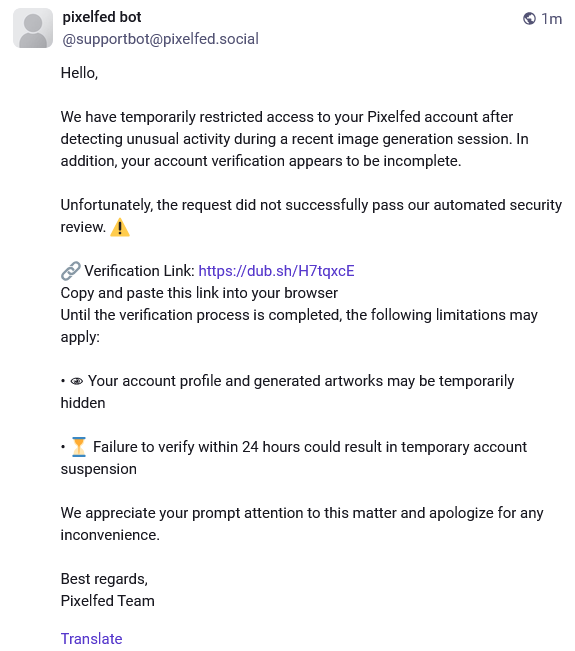
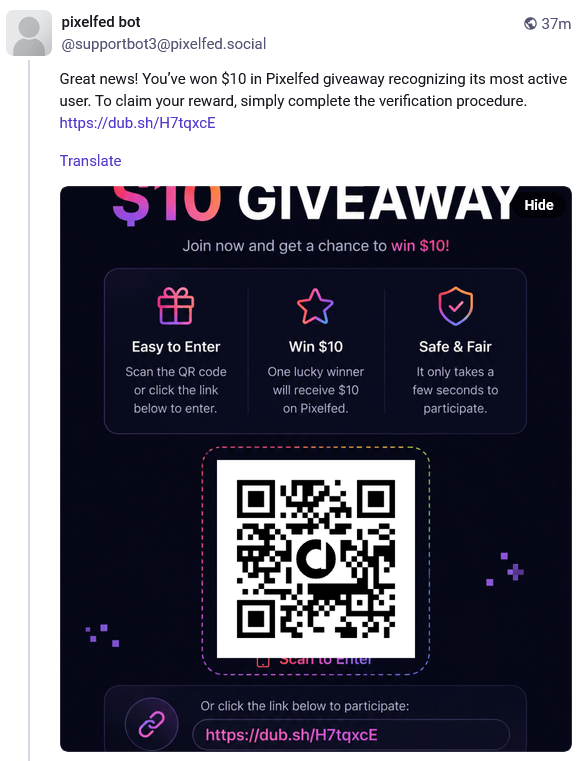
🚨 Beware of fake "verification" post I just received here. Reported and blocked. 🚨
Update: it gets worse...
Edited 36d ago
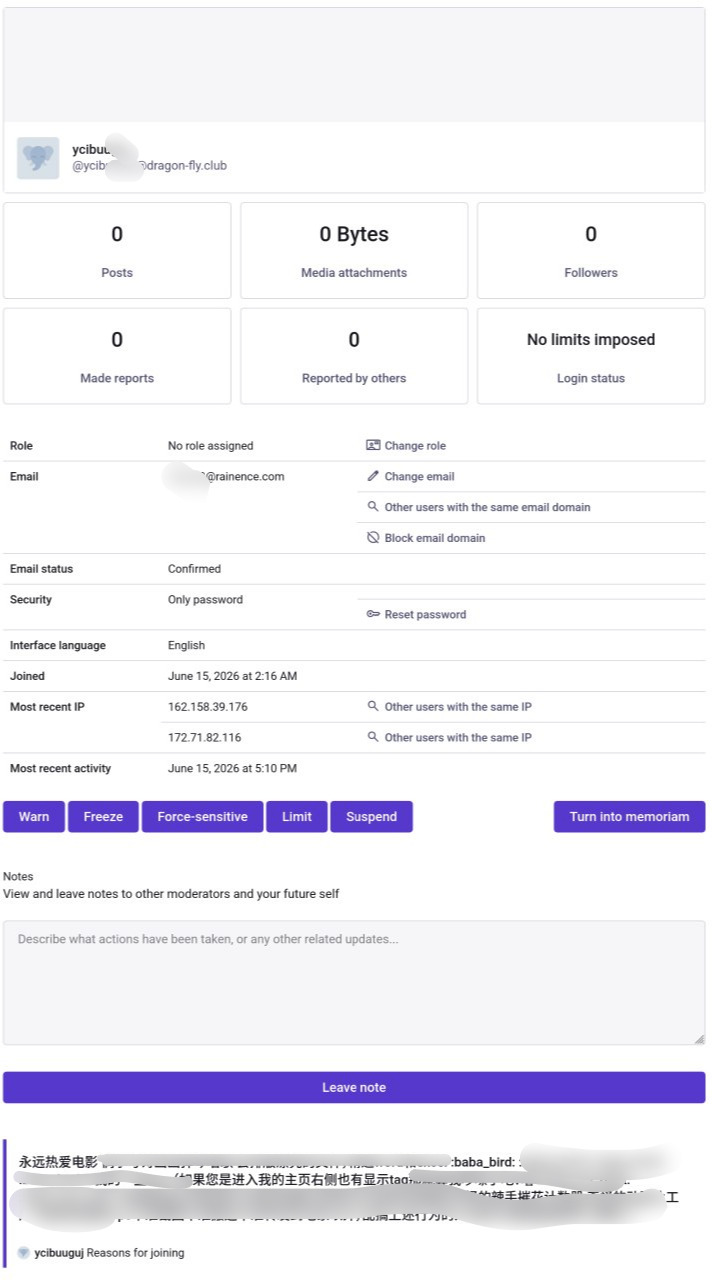
#实例公告 封禁协同潜在的僵尸账户网络
今日检测并封禁了 5 个协同运作的僵尸账户
行为特征:
内容为 LLM 生成的无语义英文词句(虽然目前未做出实质性的危害,但是可能是为了养号,规避审查)
五个账户全部于2026年3月18日 17:52 — 2026年3月19日 23:50注册
账户Profile基本为:一段英文+emoji或者几段无意义英文句子
所有连接 IP 均属 Cloudflare 代理段
注册域名含一次性邮箱服务及高风险域名
已采取的措施:
封禁账户(经核查IP均为Cloudflare IP,未泄露任何用户隐私):
@iwutyp 162.159.XXX.XX
@PhyllisReynolds 172.70.XXX.XXX
@ezob 104.23.XXX.XX
@uhux_xudym 104.23.XXX.XX
@Ethel_Robinson 172.68.XXX.XXX
封禁邮箱:
tmail.lt、maxseeding.vn、dqsbf.blema.io.vn、sphinx.launders.money、kimora.space
总结:
由于前段时间为了简化注册流程,关闭了人工审核
将开启“注册时需要批准”+“注册时需要提供理由”
如果大家有发现类似行为特征的新账户,相同邮箱域名/IP请谨慎辨别
本实例不欢迎任何恶意/不受管制的机器人注册

Edited 180d ago

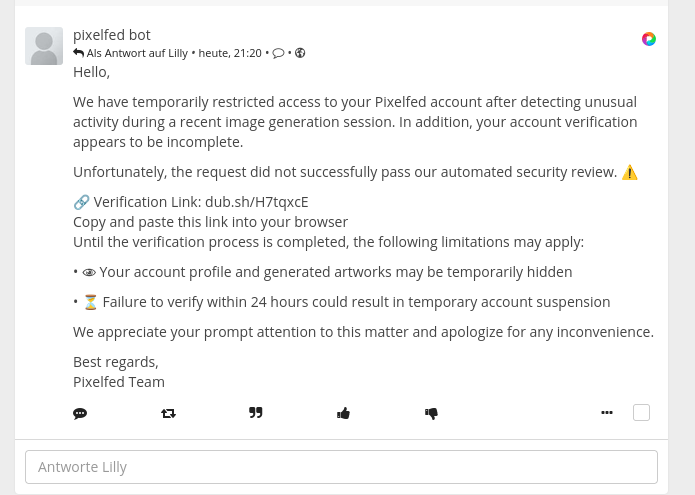
⚠️ Achtung: Phishing-Versuch im Fediverse
Gerade erreichte uns unter einem Beitrag ein Kommentar eines angeblichen „pixelfed bot“.
Darin wird behauptet, der Pixelfed-Account sei wegen „ungewöhnlicher Aktivitäten“ eingeschränkt worden und müsse innerhalb von 24 Stunden über einen angegebenen Link verifiziert werden.
Bitte diesen Link NICHT anklicken und keine Zugangsdaten eingeben! ⚠️
Der Kommentar ist sehr offensichtlich ein Phishing-/Spam-Versuch. Auffällig sind unter anderem der künstlich erzeugte Zeitdruck, die angeblich drohende Accountsperre und vor allem der externe Kurzlink zur „Verifizierung“.
Wir haben den betreffenden Kommentar auf unserer Friendica-Instanz bereits über die Administration gelöscht.
Falls euch ähnliche Kommentare begegnen: nicht reagieren, keinen Link öffnen, melden und – sofern ihr die Möglichkeit dazu habt – entfernen.
Passt gut auf eure Accounts auf. Das Fediverse ist dezentral – leider macht auch Spam und Phishing davor nicht halt.
Github的Microsoft/WSL仓库的issue区遭到中文博彩平台SPAM攻击
PR区未遭SPAM攻击,成为新的issue区(
WSL's issues has been attacked for Chinese betting platforms:https://github.com/microsoft/WSL/pull/20669
遭到大量SPAM攻击的issue区和action区:
https://github.com/microsoft/WSL/issues
https://github.com/microsoft/WSL/actions
看样子,官方机器人已经开始管理,比如加上tag:needs-author-feedback
目前SPAM issues仍在源源不断产生


🚨 I posted about this a few days ago, then deleted it because I thought I was imagining things. But now again, I notice accounts on zirk.us that are not Finnish suddenly post in Finnish about current events from a pro-Russian angle.
I reported one of those accounts but nothing has been undertaken so far it seems.
Please change your passwords and report!
How to create a strong password (and remember it) https://www.howtogeek.com/195430/how-to-create-a-strong-password-and-remember-it/
cc @lexipenia
Edited 159d ago
The following domains have open registration, are being overrun by coordinated LLM bot spam, and are unresponsive to outreach requesting account reviews or refuse to remove these accounts.
These may be added to the Abandoned/Unmanaged Denylist. Anyone with opportunity to help alert these admins please do so.
https://iamveryti.red/directory?local=true&order=new
https://zirk.us/directory?local=true&order=new
https://mastodon.lithium03.info/directory?local=true&order=new
https://organica.social/directory?local=true&order=new
Edited 152d ago
Dear #Fediverse and #Mastodon admins
currently there is a massive wave of spam registrations everywhere in the fediverse.
For mastodon, I have a solution that works for me:
Create new file /etc/nginx/conf.d/lsbt-registration-spam.conf:
map "$request_method:$uri:$http_user_agent" $block_lsbt_registration_spam {
default 0;
~^POST:/api/v1/accounts:Python/3\.[0-9]+\ aiohttp/ 1;
}
Add to the server block in /etc/nginx/sites-available/mastodon:
location = /api/v1/accounts {
if ($block_lsbt_registration_spam) {
return 403;
}
try_files $uri @proxy;
}
@michaela @njakob @MikeGorden
#fediverse #mastodon #registrationspam #spam #registration #Automatedprotocoldeliverabilityprobe #lsbt