272902 – Security: allow passphrases for WPA-EAP to be saved without using clear text
security
#Hollo 0.6.0 is coming soon!
We're putting the finishing touches on our biggest security and feature update yet. Here's what's coming:
- RFC 8414 (OAuth metadata discovery)
- RFC 7636 (#PKCE support)
- Improved authorization flows following RFC 9700 best practices
New features
- Extended character limit (4K → 10K)
- Code syntax highlighting
- Customizable profile themes
- EXIF metadata stripping for privacy
Important notes for update
- Node.js 24+ required
- Updated environment variables for asset storage
- Stronger
SECRET_KEYrequirements (44+ chars)
Special thanks to @thisismissem for the extensive OAuth improvements that help keep the #fediverse secure and compatible! 🙏
Full changelog and upgrade guide coming with the release.
In related news, #Hollo has also released #security updates: 0.3.6 & 0.4.4. Update now!
https://hollo.social/@fedify/01948487-87b2-709d-953f-8799b78433ed
We have released #security updates (1.0.14, 1.1.11, 1.2.11, 1.3.4) to address CVE-2025-23221, a #vulnerability in #Fedify's #WebFinger implementation. We recommend all users update to the latest version of their respective release series immediately.
The Vulnerability
A security researcher identified multiple security issues in Fedify's lookupWebFinger() function that could be exploited to:
- Perform denial of service attacks through infinite redirect loops
- Execute server-side request forgery (#SSRF) attacks via redirects to private network addresses
- Access unintended URL schemes through redirect manipulation
Fixed Versions
- 1.3.x series: Update to 1.3.4
- 1.2.x series: Update to 1.2.11
- 1.1.x series: Update to 1.1.11
- 1.0.x series: Update to 1.0.14
Changes
The security updates implement the following fixes:
- Added a maximum redirect limit (5) to prevent infinite redirect loops
- Restricted redirects to only follow the same scheme as the original request (HTTP/HTTPS)
- Blocked redirects to private network addresses to prevent SSRF attacks
How to Update
To update to the latest secure version:
# For npm users
npm update @fedify/fedify

# For Deno users
deno add jsr:@fedify/fedify
We thank the security researcher who responsibly disclosed this vulnerability, allowing us to address these issues promptly.
For more details about this vulnerability, please refer to our security advisory.
If you have any questions or concerns, please don't hesitate to reach out through our GitHub Discussions, join our Matrix chat space, or our Discord server.
#DrunkRapist #PeteHegseth readies *actions* against #Trump “foe” Retired General & former chairman of the #JointChiefsOfStaff #MarkMilley
The retired general, a frequent target of #Trump, will lose his #security detail & face an #InspectorGeneral [apparently there’s one left] investigation, said a senior #defense official.
#military #jcs #honor #integrity #IG #RevengePolitics #law #USpol
https://www.washingtonpost.com/national-security/2025/01/28/mark-milley-hegseth-trump/
Facebook flags Linux topics as 'cybersecurity threats' — posts and users being blocked
#news #tech #technology #socialmedia #facebook #linux #security
Unbelievable
#ElonMusk’s US #DOGE Service are feeding sensitive data into #AI software via #Microsoft’s #cloud
#Musk’s US #DOGE Service have fed sensitive data from across the #Education Dept into #ArtificialIntelligence software to probe the agency’s programs & spending…. The AI probe includes data w/personally identifiable info for people who manage grants, & sensitive internal financial data…
#law #security #InfoSec #CyberSecurity #NationalSecurity #Trump #TrumpCoup
https://www.washingtonpost.com/nation/2025/02/06/elon-musk-doge-ai-department-education/
“The Intern in Charge”: Meet the 22-Year-Old Trump’s Team Picked to Lead Terrorism Prevention
—
One year out of college and with no apparent national security expertise, Thomas Fugate is the Department of Homeland Security official tasked with overseeing the government’s main hub for combating violent extremism.
https://www.propublica.org/article/trump-dhs-thomas-fugate-cp3-terrorism-prevention?utm_source=mastodon&utm_medium=social&utm_campaign=mastodon-post
#News #DHS #Extremism #Trump #Security #Terrorism #Government
RE: https://mastodon.social/@arstechnica/117474965298507276
How the fuck could a certificate authority be so fucking moronic? Update your browsers people, if your OS allows it, distrust these certs system wide. If you're using Edge, don't (if that already wasn't obvious).
I submitted a Pull Request to update MacPorts' OpenSSH to 9.9p2 here:
https://github.com/macports/macports-ports/pull/27712
GitHub Continuous Integration checks are running. Hopefully they will be OK (Update 2 out of 3 have completed successfully, which is a good sign).
I tested locally without issues, but I also build against LibreSSL locally, whereas GitHub CI and MacPorts' Build Bots I think default to OpenSSL.
This release is to address some vulnerabilities identified by Qualys and other less critical bugs.
More details from upstream here:
https://www.openssh.com/releasenotes.html#9.9p2
Of particular note:
" Fix CVE-2025-26465 - ssh(1) in OpenSSH versions 6.8p1 to 9.9p1
(inclusive) contained a logic error that allowed an on-path
attacker (a.k.a MITM) to impersonate any server when the
VerifyHostKeyDNS option is enabled. This option is off by default.
* Fix CVE-2025-26466 - sshd(8) in OpenSSH versions 9.5p1 to 9.9p1
(inclusive) is vulnerable to a memory/CPU denial-of-service related
to the handling of SSH2MSGPING packets. This condition may be
mitigated using the existing PerSourcePenalties feature.
Both vulnerabilities were discovered and demonstrated to be exploitable
by the Qualys Security Advisory team. We thank them for their detailed
review of OpenSSH."
If I read everything correctly, these vulnerabilities primarily only impact the Portable OpenSSH releases (which is what MacPorts uses). However, OpenBSD has also issued the following errata to mitigate one of the issues as it also appears to impact OpenBSD users:
"008: SECURITY FIX: February 18, 2025 All architectures
sshd(8) denial of service relating to SSH2MSGPING handling. ssh(1) server impersonation when VerifyHostKeyDNS enabled.
A source code patch exists which remedies this problem."
Source code patch for OpenBSD here:
https://ftp.openbsd.org/pub/OpenBSD/patches/7.6/common/008_ssh.patch.sig
Having written as much, it appears as if the main OpenSSH version for OpenBSD is still 9.9, so I am not going to make a submission for undeadly.org Other editors reading this are welcome to though, I just kind of have a lot of other stuff on my plate at present.
As usual, I also have too much going on in my life to want more responsibilities such as commit access within MacPorts, so it's up to someone else to merge it.
Update #2: I also decided to be a good Samaritan and reported the issue to Apple. Not that they have ever acknowledged my efforts for such things nor paid me from their bug bounty program in years of doing similar things. Because, OFC, Apple can't spare a penny to anyone like me. Maybe Qualys already reported it to them anyway (though they would have no obligation to do so, they did find the vulns and reported them upstream as would be expected).
#OpenSSH #MacPorts #SecureShell #InfoSec #Cryptography #Security #CVE #PatchTuesday #OpenSource #OpenBSD #macOS
Edited 1y ago
We're Privacy Guides, a non-profit project & community focused on personal data security and privacy. 👋
Much like the right to interracial marriage, woman's suffrage, freedom of speech, and many others, our right to privacy hasn't always been upheld. In several dictatorships, it still isn't. Generations before ours fought for our right to privacy. Privacy is a human right, inherent to all of us, that we are entitled to (without discrimination).
You shouldn't confuse privacy with secrecy. We know what happens in the bathroom, but you still close the door. That's because you want privacy, not secrecy. Everyone has something to protect. Privacy is something that makes us human.
We're on a mission to inform the public about the value of digital privacy, and about global government initiatives which aim to monitor your online activity.
Angenommen es gäbe nur diese beiden Messenger, welchen würdet ihr bevorzugen?
#messenger #signal #threema #sicherheit #security
Options: (choose one)
Edited 1y ago
❌ You can't trade privacy to prevent crime.
⚠️ Message scanning tech punches a hole in everyone's security. Surveillance organisations, hackers, scammers and predators alike will be able to creep into your life.
Read our longread on the need to protect end-to-end encryption ⬇️
#PracticeSafeText #e2ee #encryption #OnlineSafetyAct #privacy #security
https://www.openrightsgroup.org/blog/the-case-for-encryption/
@GrapheneOS is being threatened by French authorities for refusing to add backdoors and they're dealing with coordinated attacks in French media right now. They're pulling out of France entirely, moving all their servers, and fighting off a wave of bullshit one-sided reporting that makes them look like they're helping criminals.
They need us to fight back. Support them however you can, whether that's a dollar, sharing their story, pushing back on the garbage news coverage when you see it, or just telling someone you know about what's happening. All of it matters because they're drowning in attacks from governments and media and bad actors who want them gone.
This is the only Android OS that actually makes me feel like privacy isn't just marketing. They fight for us now they need us to fight for them.
The EU is pushing Chat Control and creating an environment where governments feel empowered to threaten developers into compliance, and if we stay quiet we're letting it happen. Show up for them in whatever way you're able to.
#grapheneos #Privacy #NoBackdoors #encryption #security #chatControl
Edited 341d ago
🚨 Time is Running Out to Save Encryption 🔐
Ofcom is consulting on implementing message scanning powers in the UK Online Safety Act.
This would break end-to-end encryption on the messaging apps we all use!
⏰ CLOSES Monday 10 March, 5pm.
Use our tool to tell Ofcom #PracticeSafeText 💬
ACT NOW ⬇️
https://action.openrightsgroup.org/48-hours-tell-ofcom-practice-safe-text
#e2ee #encryption #OnlineSafetyAct #ukpolitics #ukpol #privacy #ofcom #security #cybersecurity #whatsapp #signal
Edited 1y ago
I just published “Generating Passphrases Like correct horse battery staple” at
https://www.ii.com/passphrase-generators/ - please post suggestions for passphrase generators as a reply to this toot and I'll include them in my article!
#InfiniteInk #Privacy #Security #Tech #Passwords #Passphrases #CorrectHorseBatteryStaple
#Words #Writing #Byℵ #ByNM
"Noem isn’t doing homeland #security. I’m not sure she knows its meaning. Like habeas corpus, which she thinks is an Ecuadorian offshoot of MS-13. Instead of safety and security, Noem’s turned the agency into the rabid attack dog she wanted Cricket to be"
READ MORE https://www.blueamp.co/p/were-all-cricket-and-the-united-states #news #usa #politics #dhs #ice #losangeles #la #tv #nato #media #press #russia #ukraine #eu us #unitedstates #america #trump #donaldtrump #cliffschecter #blueamp #cliffsnote #cliffsedge #davidshuster
If you still use one of these devices, you might want to start looking into alternatives.
"In an email sent to customers today, Amazon said that Echo users will no longer be able to set their devices to process Alexa requests locally [...] Starting on March 28, recordings of everything command spoken to the Alexa living in Echo speakers and smart displays will automatically be sent to Amazon and processed in the cloud."
via https://mamot.fr/@pluralistic/114166991733057284
#news #TechNews #technology #amazon #alexa #AmazonEcho #privacy #security
tj-actions/changed-files 被骇,被骇版本会将 secret 写入运行日志;现已修复。
- 骇客伪装成 Renovate bot 更新了 minify 的 Actions 代码,亦修改了所有 tag 使其指向恶意 commit。
- 维护者称原因是自己的一个 PAT (Personal Access Token) 泄露 [1]。
- gh:tj-actions/changed-files#2463
- stepsecurity.io/~
1. gh:tj-actions/changed-files#2464
#Security #GitHubActions
Telegram 原文
 🎃👻
Great, informative writeup of Cryptographic Gotchas: https://gotchas.salusa.dev/
Lots of fantastic references and links in there, too.
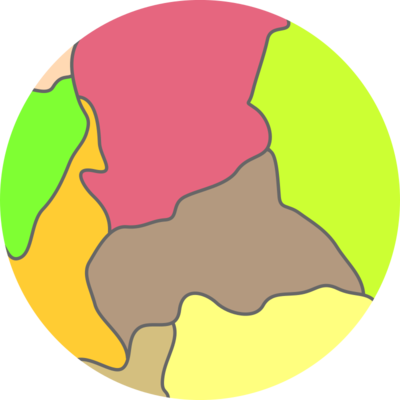
Last week we published a set of three in-depth #map reports covering territorial control across #Somalia's claimed territories from 2023 to present. The June 2024 report is free for all readers, and shows the height of "#IslamicState" (#ISIS/#ISIL) control in the country:
https://www.polgeonow.com/2025/06/somalia-territorial-control-map-2024-isis-shabaab.html
#HornOfAfrica #cartography #maps #geography #Somaliland #Puntland #SSC_Khaatumo #mapping @geography @cartography @geopolitics #AlShabaab #AlQaeda #security #OSINT
Killing Grants That Have Saved Lives: Trump’s Cuts Signal End to Government Work on Terrorism Prevention
—
Tens of millions of dollars slated for violence prevention have been cut or are frozen as DOGE steamrolls the national security sector. “This is the government getting out of the terrorism business,” said one grant recipient.
https://www.propublica.org/article/trump-doge-budget-cuts-terrorism-prevention?utm_source=mastodon&utm_medium=social&utm_campaign=mastodon-post
#News #Terrorism #Security #Government #Trump #DOGE #USPolitics
it's been quite a while, so lemme write a new #intro
i'm raven, a silly #transgirl on the internet who likes to write, and create free-to-use #photography (mostly landscapes). u can find me on mastodon, and see what an overview of what i’m up to on my now page. i have so many interests and try my best to experience new things in this short life. some sort of neurospicy, tend to be overly genuine, a bit corny, over-opinionated at times
🩺 #nurse, 📸 #photographer, 👩💻 #linux nerd, 🏳️⚧️ #trans girl, 💞 #relationship anarchist, 🌱 #vegan for the animals, 🌹 #leftist, ✊ #union steward, 🧗♀️ #queer outdoor girlie, 🌠 star stuff, 🚴♀️ bikes are cool, 😽 certified girl/boy/nb-kisser, 😝 #silly adventurer
i work in the OR as a nurse and i love my job
likes: #forests, #mountains, #oregon coast, #coffee, #adventures, #movies, #computers, #transit, #bikes, #Portland OR, scrub-role in surgery, science-stuff, n95s, #sewing, #privacy and #security in tech, #philosophy, #ceramics, #sailing, #music, pineapple on pizza, #leftism, workers-rights, #silliness, #headpats, and #praise
“chaotic af, kinda scatter brained, but smart if that makes sense”
“very direct and able to be vulnerable very easily (a good thing!) and the most ethically-minded and community-focused person ive met!”
“an iceberg. you’ve got a fun, flirty, smolder of a vibe when people meet you initially. then after getting to talk with you people see that you’ve got way more going on under the surface of the water”
i upload my photography as creative commons attribution license, i don't own a car, i have a #cat named Loki who i post about under the #catsofmastodon tag, i'm #divorced after a 14 year marriage (not the outcome i wanted, but here i am), and now happily in relationships as a relationship anarchist.
i live in #pdx and want to make it a better place by organizing and creating #unions and #community
i do #rock-climbing, #bjj, #running, #swimming, #sailing, currently recovering from injuries
i love #webdesign and created a #hugo theme which i use for my website (on github)
yes, imma #puppygirl and silly af
Edited 1y ago
Getting started with XMPP/Jabber and PGP for federated, encrypted messaging
This is a short thread where I explain how I started using the XMPP protocol and PGP encryption for secure messaging. I am not a security expert, but I am a mathematician and I am confortable with the Linux command line. This guide is for people who want to use PGP for secure messaging easily. You will need to be okay with typing commands into the Linux command line in order to do this, but I will tell you exactly what to enter.
Part 1: XMPP
Mastodon is like email, but for social media. You sign up for an account with a server, and then you can talk with any other accounts that are signed up on other servers, as long as your servers are getting along. (No one wants emails from the sketchy spam server, and we want to be able to choose between Yahoo, Gmail, etc.) XMPP (a.k.a. Jabber) is the same thing for text messaging.
Just like signing up for an email/Mastodon account, you need to sign up for an account. You can find a list of servers at https://list.jabber.at/ and will probably at least need to provide an email addess when making an account.
Once you have made an account, you need a client. On Linux, I've been having a good time using Dino (https://dino.im/). You can then enter your account name and password to log into your XMPP account and start chatting! There are both public rooms and you can also message directly with your friends.
#security #PGP #XMPP #FOSS #Jabber #Dino #MonoclesChat
(1/4)
A list of Digital Service Providers located outside the jurisdiction of the United States of America:
https://codeberg.org/Linux-Is-Best/Outside_Us_Jurisdiction
This is an ongoing group project — so if you have any suggestions, corrections, or new information to share, feel free to reach out!
#USJurisdiction #USA #America #UnitedStates #Privacy #Security