I've leveled up my home network and it means only one thing: a new cringe-worthy WiFi name.
Moving on from "Make WiFi Great Again"... the new SSID is:
"It Hurts when IP"
Send me your best/worst tech puns, I need more! 👇
I've leveled up my home network and it means only one thing: a new cringe-worthy WiFi name.
Moving on from "Make WiFi Great Again"... the new SSID is:
"It Hurts when IP"
Send me your best/worst tech puns, I need more! 👇
This morning, I took my wife to the hospital for routine blood tests that had been scheduled for some time. Everything was going smoothly: check-in, number, waiting room. Suddenly, everything came to a halt and shut down. I was connected to the hospital’s public Wi-Fi and noticed that my connection also went down.
Having managed a couple of similar facilities, I immediately understood what had happened. I saw the staff panicking and calling the technicians, but they quickly reorganized within 10 minutes. They managed to process everyone who already had a number and then proceeded with the others in the order of their arrival. Despite the ten-minute delay (even though people started complaining right away), they were extremely efficient.
I later confirmed that the entire booking, check-in, and queue system is “in the cloud.” The hospital experienced a connectivity interruption, and all related services stopped. The staff no longer had access to anything, so a technician sent the lists to a manager via another channel, and everything resumed manually.
For years, I’ve insisted that certain things MUST be local. The healthcare facilities I manage have all the necessary systems for the operation of the facility internally, including patient records. External services like websites, emails, etc., are secondary.
Everything essential must always be accessible locally and, in special cases, it should be possible to physically access the servers and connect directly to them, bypassing any network/switch failures.
There has been only one interruption in the past, due to human error. Today, we have redundant servers (not HA on virtualizers, but two machines running the same software with replicated databases - on separate power lines) so such an issue shouldn’t happen anymore.
Not everything can be anticipated, but history is a great teacher. The Internet connection will eventually be interrupted :-)
When it comes to the health and survival of people, there are no compromises.
#IT #Internet #Networking #Outage #Health #HA #Cloud #CloudComputing #OwnYourData
Sometimes surprises come when you least expect them. A few months ago, I helped an acquaintance install a #MikroTik router at his house. He is very happy with it; it does excellent load balancing and failover over 4G.
A little while ago, he sent me a message about how "Back to Home" helped him bypass the limited connection at the hotel he is currently in.
I hadn't tried it yet, so I did a couple of tests.
It's really practical and quick to set up. Well done, MikroTik! @mikrotik
One day, we will read about the heroic efforts Palestinian networking engineers did throughout experiencing genocide to keep the network routers on, the cables connected, and getting the signal out there.
Actual war stories on a hope that we hear them asking is anyone out there who will help them. #Networking #Palestine #Genocide #DevOps
OSPF area types.
Backbone
Stub
Totally stubby
Not so stubby
Totally not so stubby (yes, it really is a thing).
My proposed OSPF areas.
Not so backbone
Thighbone
Lovebone
So-so stubby
Not so so-so stubby
totally not so totally stubby
tubular
totally tubular
not so tubular
totally not so tubular and stubby
A continuation of the same idea
I had already explored the same problem with snac and nginx in two previous posts: Improving snac Performance with Nginx Proxy Cache (https://it-notes.dragas.net/2025/01/29/improving-snac-performance-with-nginx-proxy-cache/) and Caching snac Proxied Media with Nginx (https://it-notes.dragas.net/2025/02/08/caching-snac-proxied-media-with-nginx/). In both cases, the idea was that the reverse proxy should absorb repeated public requests instead of letting them consume snac resources.Why there is almost no media
Before talking about HAProxy, it is worth mentioning one of the most important optimizations, which is not in the proxy configuration at all.The homepage is static because it can be static
The main homepage follows the same logic.Many countries, one entry point
FediMeteo is made of many country instances. Each one runs in its own jail and listens on its own internal address and port. From the outside, however, they all live under the same domain structure:fedimeteo.com
www.fedimeteo.com
it.fedimeteo.com
uk.fedimeteo.com
jp.fedimeteo.com
us.fedimeteo.com
usa.fedimeteo.com
can.fedimeteo.com
canada.fedimeteo.com
fedimeteo.com backend_fedimeteo
www.fedimeteo.com backend_fedimeteo
it.fedimeteo.com backend_it
uk.fedimeteo.com backend_uk
jp.fedimeteo.com backend_jp
us.fedimeteo.com backend_us
usa.fedimeteo.com backend_us
can.fedimeteo.com backend_ca
canada.fedimeteo.com backend_ca
use_backend %[req.hdr(host),field(1,:),lower,map(/usr/local/etc/fedimeteo.map,backend_fedimeteo)]
Backends as small compartments
The country backends are deliberately plain:backend backend_it
mode http
http-reuse safe
server srv1 10.0.0.2:8001 maxconn 30
backend backend_uk
mode http
http-reuse safe
server srv1 10.0.0.7:8001 maxconn 30
backend backend_jp
mode http
http-reuse safe
server srv1 10.0.0.32:8001 maxconn 30
The front door
The HTTPS frontend listens on IPv4 and IPv6 and offers both HTTP/2 and HTTP/1.1:frontend https_in
bind :::443 v4v6 ssl crt /usr/local/etc/certs/ alpn h2,http/1.1
mode http
option http-keep-alive
ssl-default-bind-ciphersuites TLS_AES_128_GCM_SHA256:TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256
ssl-default-bind-options no-sslv3 no-tlsv10 no-tlsv11 no-tls-tickets
acl letsencrypt-acl path_beg /.well-known/acme-challenge/
http-request redirect scheme https code 301 unless letsencrypt-acl
use_backend letsencrypt-backend if letsencrypt-acl
http-request set-header X-Real-IP %[src]
http-request set-header X-Forwarded-Proto https
http-response set-header Strict-Transport-Security "max-age=31536000; includeSubDomains; preload"
Two caches, because the requests are different
The HAProxy configuration defines two caches:cache mediacache
total-max-size 128
max-object-size 10000000
max-age 3600
process-vary on
max-secondary-entries 12
cache jsoncache
total-max-size 16
max-object-size 1000000
max-age 60
process-vary on
max-secondary-entries 12
Recognizing media
For media, the ACL is based on file extensions:acl is_media path_end -i .jpg .jpeg .png .gif .webp .svg .ico .mp4 .webm .mp3 .ogg .wav .flac .mov .avi .mkv .m4v
http-request set-var(txn.is_media) bool(true) if is_media
http-request cache-use mediacache if { var(txn.is_media) -m bool true }
http-response set-header Cache-Control "max-age=3600, public" if { var(txn.is_media) -m bool true }
http-response del-header Set-Cookie if { var(txn.is_media) -m bool true }
http-response del-header Vary if { var(txn.is_media) -m bool true }
http-response cache-store mediacache if { var(txn.is_media) -m bool true }
http-request del-header Authorization if { var(txn.is_media) -m bool true }
http-request del-header Cookie if { var(txn.is_media) -m bool true }
ActivityPub JSON microcaching
The ActivityPub side starts from the Accept header:acl is_ap_json req.hdr(Accept),lower -m sub application/activity+json
acl is_ap_ldjson req.hdr(Accept),lower -m sub application/ld+json
acl is_outbox path_end /outbox
acl is_get method GET
acl has_auth req.hdr(Authorization) -m found
acl has_cookie req.hdr(Cookie) -m found
http-request set-var(txn.is_activitypub) bool(true) if is_get !is_outbox is_ap_json !has_auth !has_cookie
http-request set-var(txn.is_activitypub) bool(true) if is_get !is_outbox is_ap_ldjson !has_auth !has_cookie
http-request cache-use jsoncache if { var(txn.is_activitypub) -m bool true }
http-response set-header Cache-Control "max-age=60, public" if { var(txn.is_activitypub) -m bool true }
http-response cache-store jsoncache if { var(txn.is_activitypub) -m bool true }
Static media paths
There is also a rule for static paths:acl is_short_path path_reg ^/[^/]+/s/
http-request cache-use mediacache if is_short_path
Vary, but not without limits
Both caches have:process-vary on
max-secondary-entries 12
Seeing whether it works
During rollout, I like to expose a very small diagnostic header:http-response set-header X-Cache-Status HIT if !{ srv_id -m found }
http-response set-header X-Cache-Status MISS if { srv_id -m found }
curl -I https://it.fedimeteo.com/path/to/avatar.png
curl -I https://it.fedimeteo.com/path/to/avatar.png
curl -I \
-H 'Accept: application/activity+json' \
https://it.fedimeteo.com/some/activitypub/object
curl -I \
-H 'Cookie: test=value' \
-H 'Accept: application/activity+json' \
https://it.fedimeteo.com/some/activitypub/object
curl -I \
-H 'Authorization: Bearer fake' \
-H 'Accept: application/activity+json' \
https://it.fedimeteo.com/some/activitypub/object
Compression and operational paths
HAProxy also handles gzip compression:filter compression
compression algo gzip
compression type text/css text/html text/javascript application/javascript text/plain text/xml application/json application/activity+json
frontend prometheus
bind 127.0.0.1:8405
mode http
http-request use-service prometheus-exporter
no log
What this changes in practice
The nice thing about this configuration is that none of its parts is particularly surprising.Caveats
This configuration is not a universal HAProxy recipe for ActivityPub services.Conclusion
FediMeteo started as a small idea and became larger than I expected, but I still want it to feel small in the right ways. Small does not mean fragile. Small means understandable. It means that each part has a reason to exist, and that unnecessary work is removed before it becomes a problem.As a female professional, I am passionate about fostering deep, meaningful connections and pursuing collaborative synergies with other women in my field. 🏳️🌈✨ #Networking #WomenInLeadership #AuthenticConnections
curl libcurl
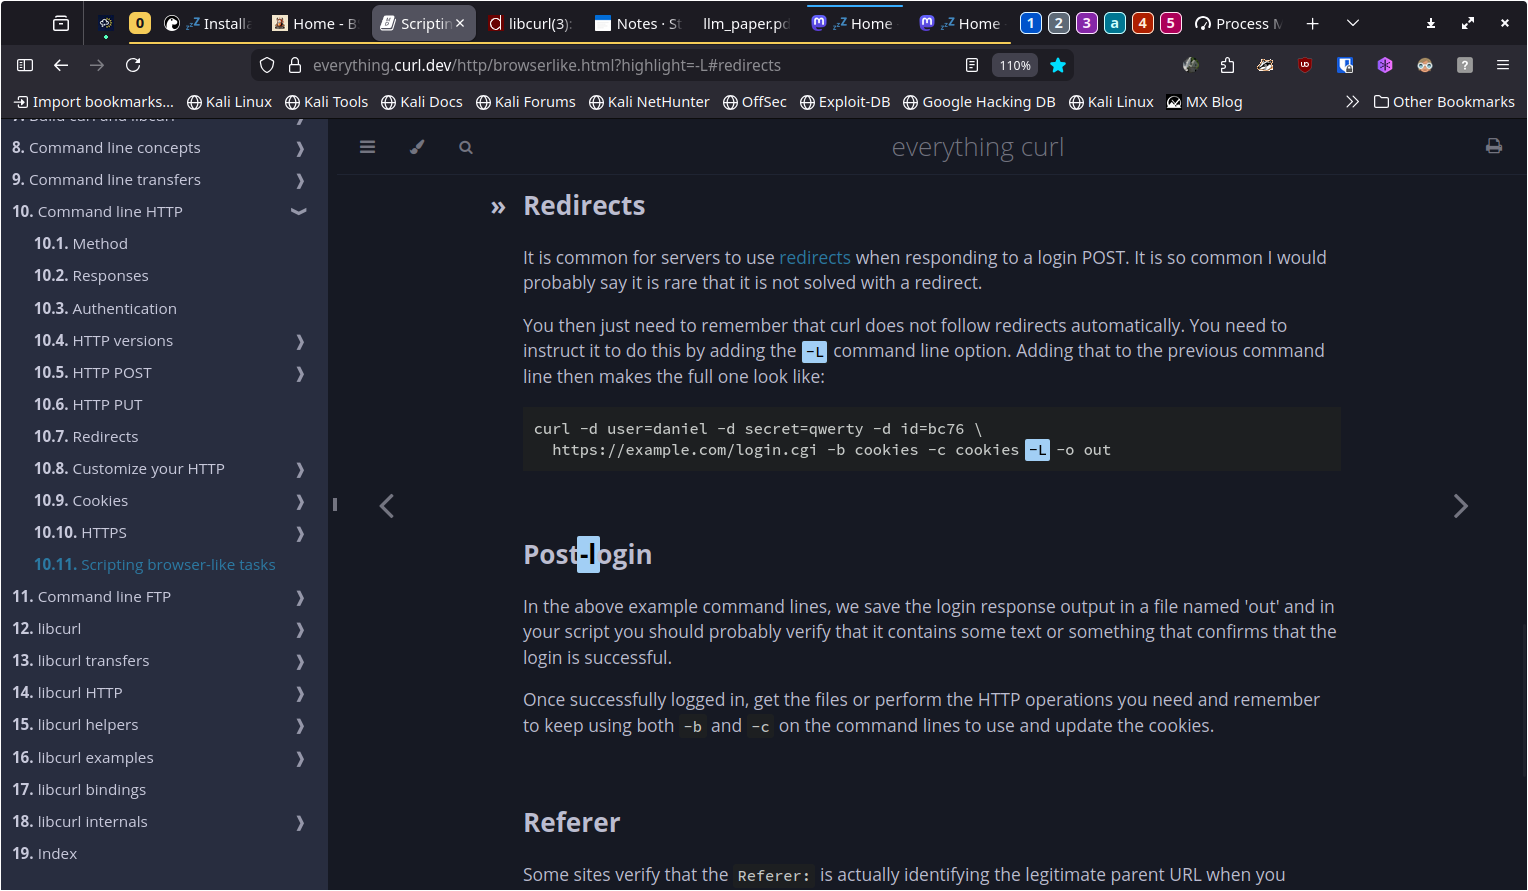
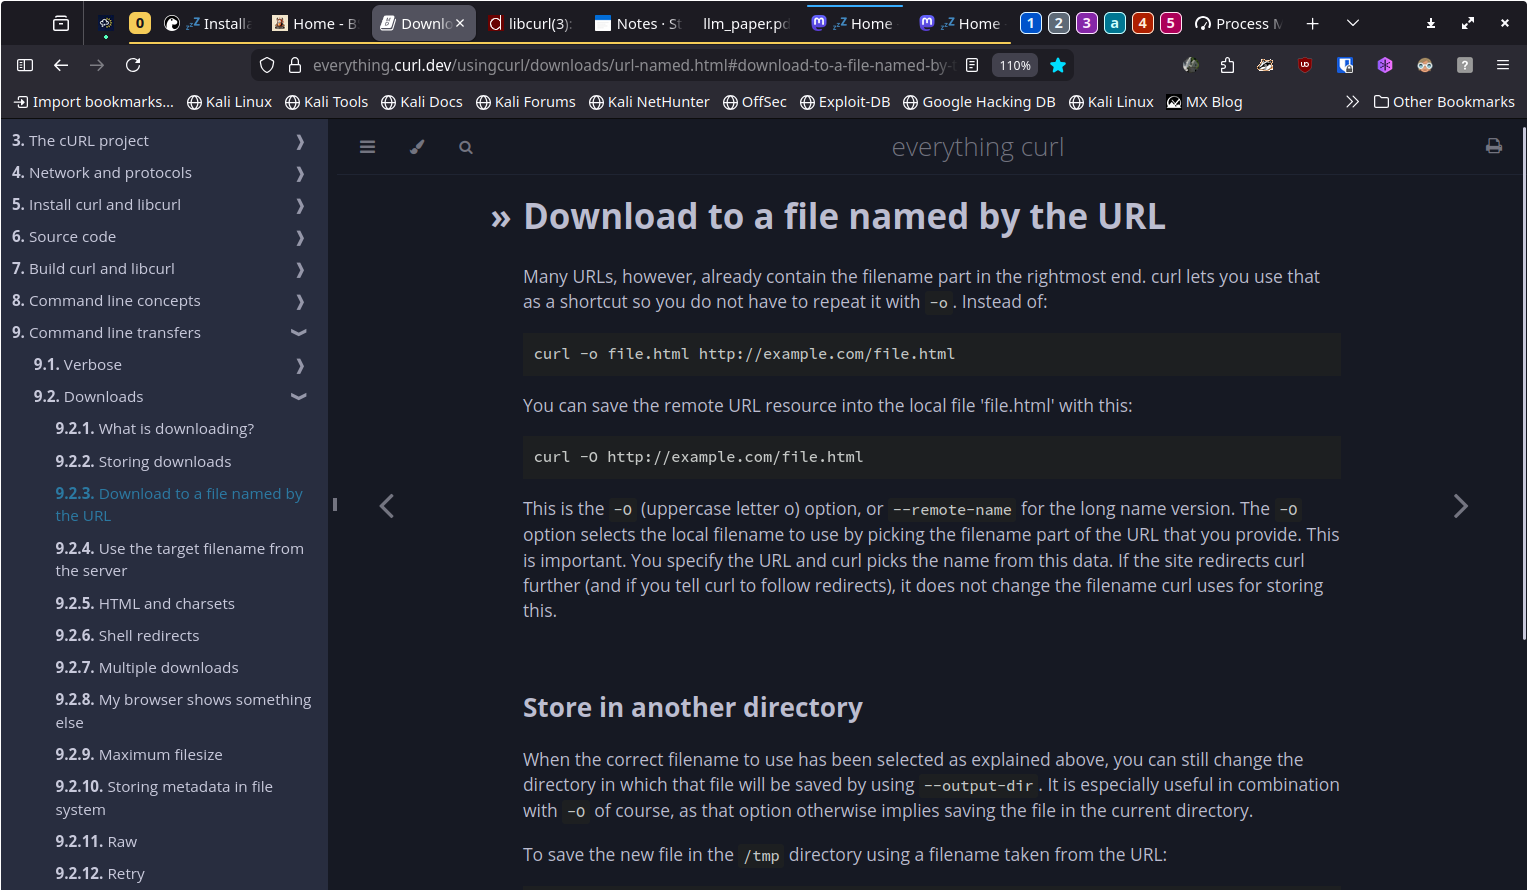
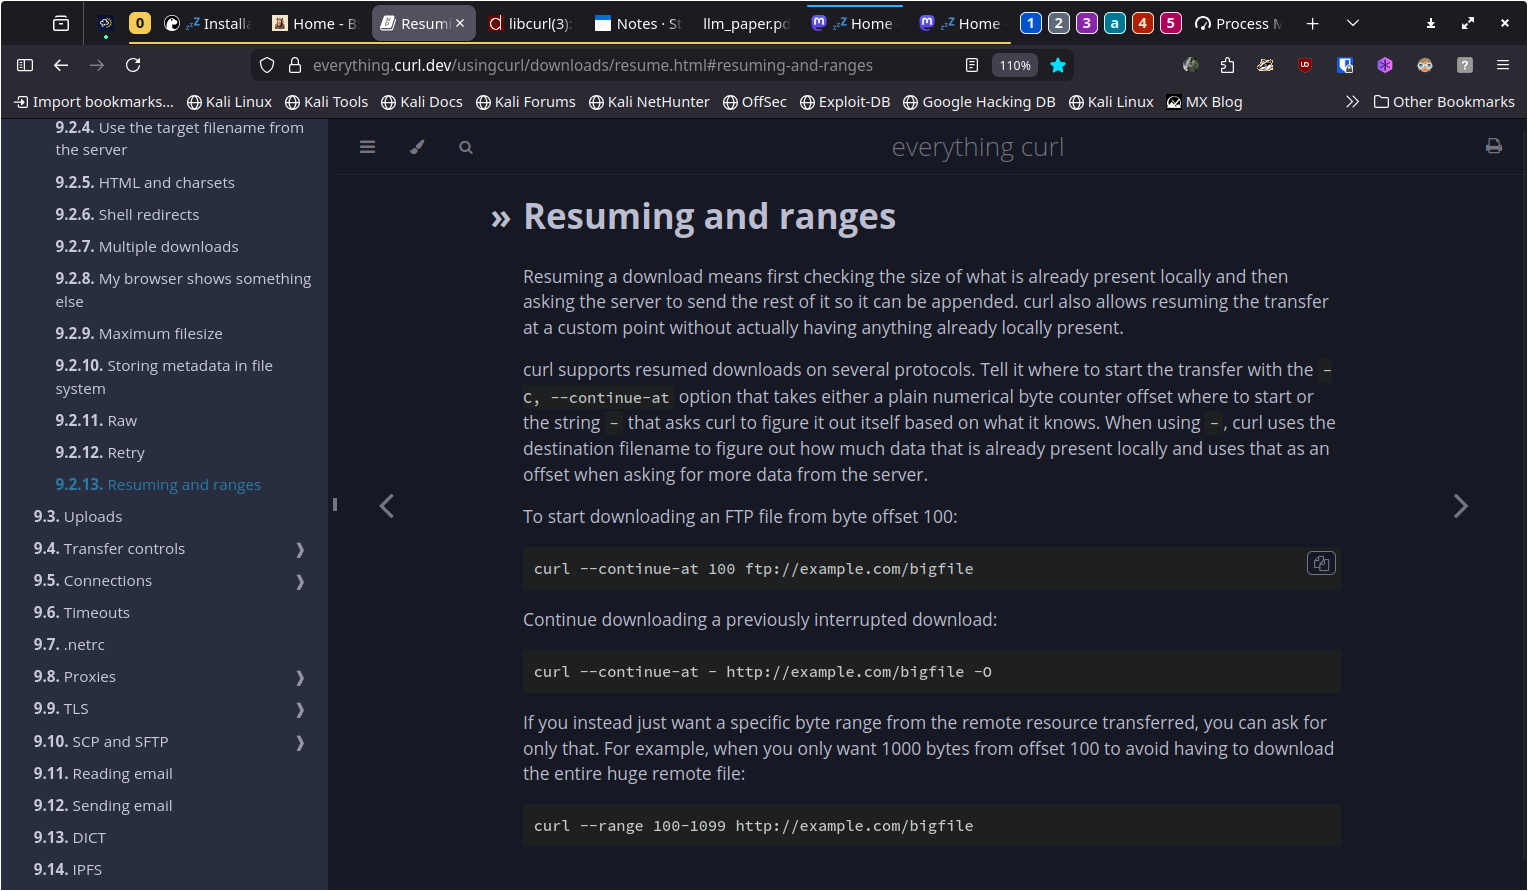
Just in case you have forgotten how to curl a file from a server here's a extensive howto with screenshots
`-L` redirect
https://everything.curl.dev/http/browserlike.html?highlight=-L#redirects
`-o` filename
https://everything.curl.dev/usingcurl/downloads/url-named.html#download-to-a-file-named-by-the-url
`-C -` resume
https://everything.curl.dev/usingcurl/downloads/resume.html#resuming-and-ranges
`curl --verbose -C - -L -o lp_someband_some_name_disc1side2.flac archive.org/download/lp_someband_somename-v/disc1/lp_someband_somename_disc1side2.flac`
#curl #get #programming #technology #fetch #networking #https #http #ftp #OpenSource #POSIX #BSD #freeBSD #ghostBSD #openBSD #Linux #win64 #mac
So it seems #LoRa is a proprietary standard. @meshtastic @meshcore @reticulum - don't we have an open drop-in alternative yet? #Zmesh?
How can we really build a resilient ecosystem for the people, when the core technology is owned by a single company?
That's like if all TCP/IP hardware was on a license from IBM.
Especially in the times of rising political tensions this looks like a bad idea.
Am I just missing something?
Source: https://aernetworks.com/blog/the-problem-with-lora-being-patented/
My latest blog post: Keeping it old school, Unix style, with inetd services!
https://mikecoats.com/simple-inetd-services/
How to build quick and dirty network services, the Unixy, way with the venerable inetd approach.
Hey people,
I recently graduated from my #SysAdmin apprenticeship and I am looking for an entry position in the field of #Linux/ #Networking Administration/Engineering or #DevOps in #NRW, #Germany (ideally around #Düsseldorf), or Remote.
As part of the apprenticeship I conducted an internship at a Neuroscience Institute of Research Centre Juelich, where I accomplished my project of automating #OpenBSD routers using #pyinfra #GitOps.
1/2
Boosts appreciated 🙏🏻
#degoogle #linux #storage #networking #cloud #homelab #privacy
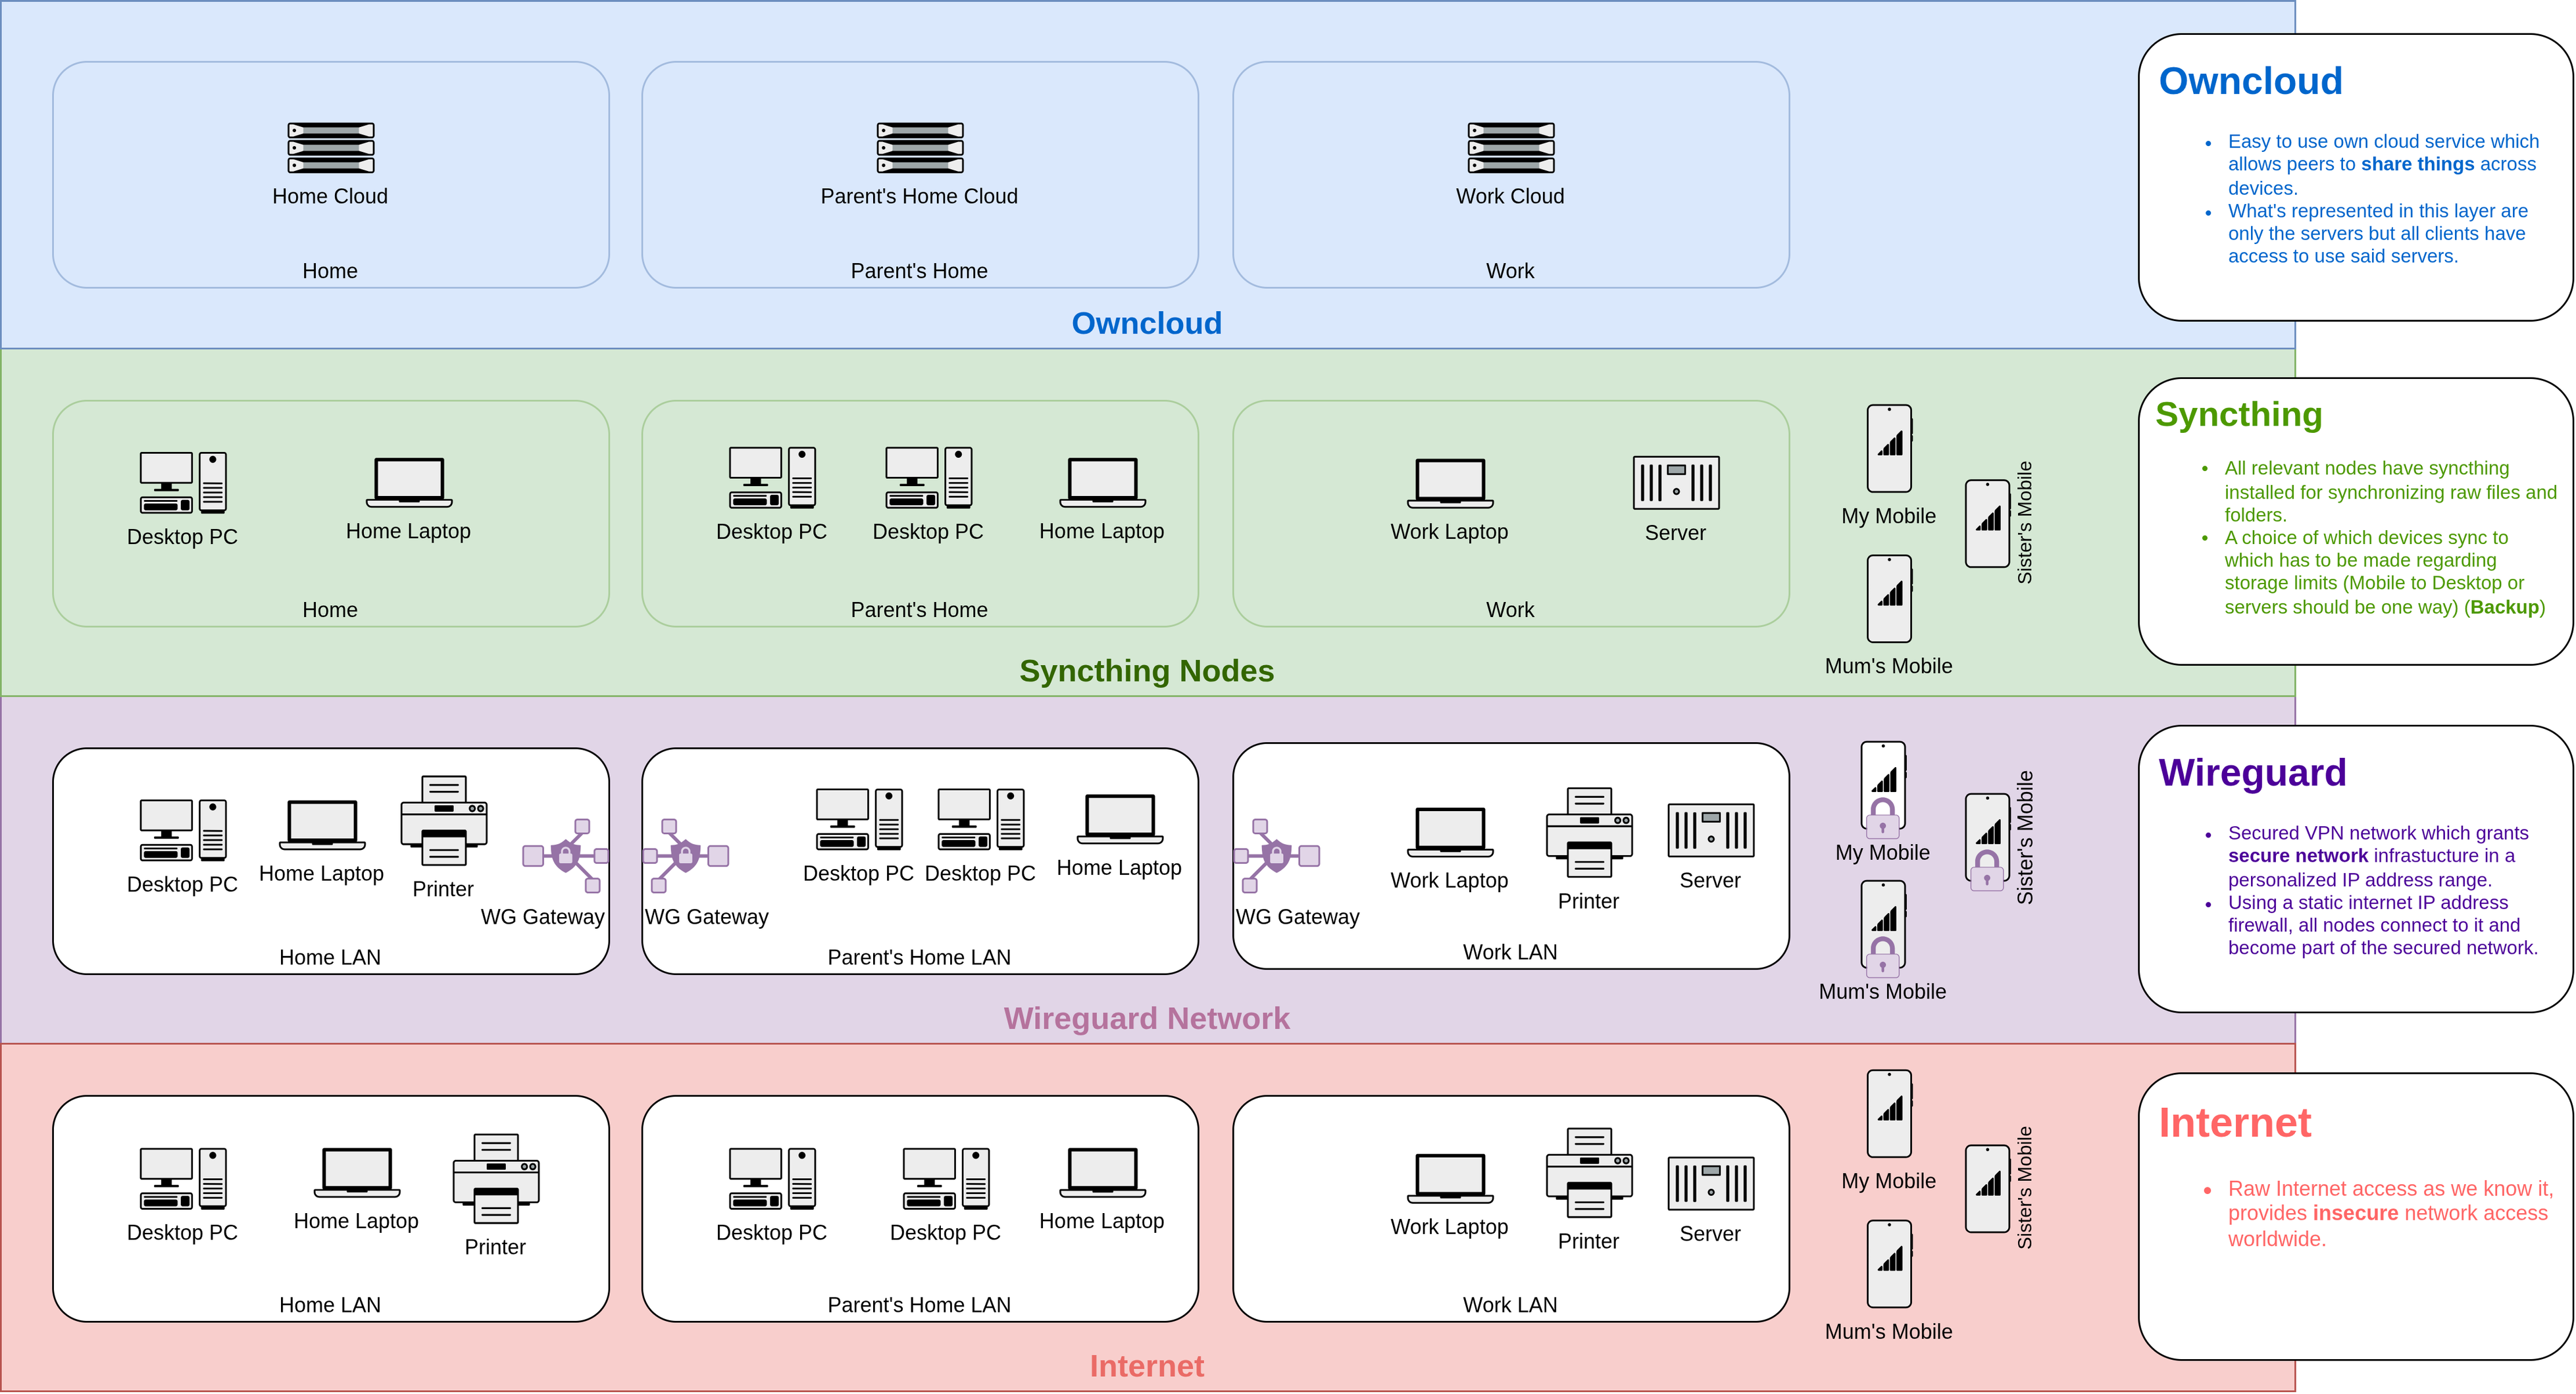
Layered schematic view of the project I'm working on for my private own cloud. Just to visualize it and for other people to see.
I'm currently working at the syncthing layer. But progress is smooth.
iptables imply the existence of ipchairs and other ipfurnitures.
You can get them at ipkea.