
Australia says OpenAI agent hacked Medicare portal | Cybersecurity News https://www.byteseu.com/2393224/ #AI #ArtificialIntelligence #AsiaPacific #Australia #Canada #China #cybersecurity #Europe #News #Privacy #Regulation #ScienceAndTechnology #Technology #UnitedKingdom #UnitedStates #US&Canada
cybersecurity
The lawsuit does not provide any technical details to back up the rather sensational claims. WhatsApp's end-to-end encryption has long been a major selling point. It means that Meta can’t decrypt and read your messages; the encryption keys are only stored on the devices that send and receive the messages.
"Any claim that people's WhatsApp messages are not encrypted is categorically false and absurd,” Meta told PCMag. “WhatsApp has been end-to-end encrypted using the Signal protocol for a decade. This lawsuit is a frivolous work of fiction and we will pursue sanctions against plaintiffs’ counsel."
The lawsuit, however, accuses Meta of trying "to prevent the truth from coming out by imposing onerous nondisclosure agreements on its workers, essentially threatening the full force of one of the world’s richest companies if any of these individuals dared reveal what goes on behind closed doors at the company. These efforts have now failed, but they worked for many, many years by obscuring the truth.”
Source: https://www.pcmag.com/news/lawsuit-alleges-that-whatsapp-has-no-end-to-end-encryption
Edited 277d ago
#Signalapp doesn't actually delete messages when they're deleted (either manually or by automation). The message deletion is written to Write-ahead Log, and the data is only truly deleted once Signal is restarted or threshold of 1000 pages is reached. For macOS Signal application, extra complication arises from the fact that the signal message database can be backed up before the database consolidation occurs. Large amount of the supposedly already deleted messages could be recovered from the device or backups.
This concerns use cases where deleting messages actually getting removed in timely manner is of high importance and recovery of the deleted messages could lead to grave consequences.
TL;DR: If you don't care about deleted messages being actually deleted you don't need to worry.
Full advisory at: https://sintonen.fi/advisories/signal-deleted-but-not-forgotten.txt
What I’ve been reading (and listening to) week ending 17 May 2026 https://medium.com/@jchyip/what-ive-been-reading-and-listening-to-week-ending-17-may-2026-677863f24825 #ai #geopolitics #cybersecurity #ProductManagement

You can now use your #Gmail account in #Proton Mail

Mystery company accidentally blew $500 million on Claude AI in a single month — failed to put usage limit on licenses for employees
A new report cites an AI consultant claiming a client accidentally spent $500,000,000 on Claude in a single month.
#Tech #Technology #TechNews #AI #Gadgets #Software #Cybersecurity #Apple #Google #Microsoft #Startup #OpenSource #TomsHardware [Tom's Hardware]

Umm, I'm pretty sure this supposed #Mastodon admin asking me to verify my account is fake, but just to concur with yall around here, that's unofficial and fake right?

Edited 254d ago
The Great American State Fair cancellations are getting framed as a culture war story. Stop there. The real signal worth tracking is what happens to event infrastructure when organizers face coordinated pressure campaigns online.
Large public gatherings tied to...
Read more: https://steelefortress.com/i10igu
Security #Cybersecurity #ThreatIntel #InfoSec
Rivian says AI makes debate over CarPlay ‘completely obsolete’
Rivian’s chief software officer, Wassym Bensaid, joined Nilay Patel in the latest Decoder interview. And his comments on CarPlay show Rivian continuing to double down on its refusal to support Apple’s platform. more…
https://9to5mac.com/2026/05/28/rivian-says-ai-makes-debate-over-carplay-completely-obsolete/
#Tech #Technology #TechNews #AI #Gadgets #Software #Cybersecurity #Apple #Google #Microsoft #Startup #OpenSource #9to5Mac [9to5Mac]
Putting VPNs behind an age wall threatens our privacy.
They keep young people safe from harassment. Business networks secure. Journalists, campaigners and whistleblowers shielded from harm.
Privacy is online safety ✊️
Sign the petition to protect VPN use in the UK ⬇️
https://action.openrightsgroup.org/tell-government-protect-vpn-use-uk
#vpn #privacy #cybersecurity #ageverification #ukpolitics #ukpol
Prywatność i cyberbezpieczeństwo to nie są hobbystyczne fanaberie dla ludzi w foliowych czapeczkach. Skompromitowane urządzenie mobilne to bezpośrednie zagrożenie dla Twojego życia osobistego, finansów i spokoju psychicznego.
Właśnie ruszyłem ze swoim blogiem, a to mój pierwszy wpis:
🔗 https://meridian.bearblog.dev/droga_do_grapheneos/
Opisuję w nim historię z ukrytym korporacyjnym MDM na moim telefonie i to, jak techniki Incident Response oraz przejście na GrapheneOS pozwoliły mi odzyskać kontrolę.
To mój debiut, dlatego bardzo zależy mi na Waszym feedbacku. Co myślicie o tym tekście? Dajcie znać w komentarzach, czy taka tematyka Was interesuje i czy chcecie kolejne wpisy o konfiguracji i hardeningu GrapheneOS! 🛡️📱
#GrapheneOS #Cybersecurity #Privacy #Prywatnosc #Bezpieczenstwo #FOSS #MobileSecurity #PlFediverse #Blog
Microsoft is required to regularly provide U.S. officials with its plan for keeping government data safe from hacking. Yet a copy of the tech giant’s security plan obtained by ProPublica makes no reference to the company’s China-based operations.
#News #Microsoft #Tech #Data #China #Cybersecurity #Government #Technology

https://www.europesays.com/3276340/ Devolutions wants to support Québec’s IT ecosystem with corporate venture capital #business #Cybersecurity #Entrepreneurship #lavaltrie #QueBasedItServicesFirmHasLaunchedAVcArmToCreateAnItEcosystem #Quebec #SaaS #VC
What I’ve been reading (, watching, and listening to) this week ending 1 March 2026 https://jchyip.medium.com/what-ive-been-reading-watching-and-listening-to-this-week-ending-1-march-2026-07be1022d9b2 #cybersecurity #strategy #misinformation #ai #management
Edited 245d ago
✨ A sparkle icon appears in an app that no one in IT approved. The help desk can't explain it, and it's already processing your data! This kept coming up in conversations with other CIOs, so I wrote about it in my latest Forbes piece.
The pattern repeats across so many vendors; here are just a few:
・Zoom auto-enabled AI Companion on host accounts, with recordings and full transcripts already defaulted on
・Microsoft 365 Copilot activates for every admin if your tenant holds a single paid license, and opting out means building a special security group
・Google's Workspace Intelligence shipped default-on for Gmail, Drive, Chat, and Calendar, with admin controls lagging the live feature by up to 72 hours
・OpenAI disables connectors by default for Enterprise customers but enables them for Business. Same vendor, opposite defaults.
Every default-on feature just transfers governance work from the vendor to you, along with wiretap exposure and e-discovery sprawl that nobody signed up for.
My ask of vendors is simple: ship AI features off by default and give admins an evaluation window measured in weeks, not days. Until that happens, assume the next AI feature is already live in your tenant. Review your configurations like it's a recurring operational task, because it is.
Full piece here: https://www.forbes.com/councils/forbestechcouncil/2026/06/10/default-on-ai-are-saas-vendors-outsourcing-their-risk-to-you
#RiskManagement #Forbes #ForbesTechnologyCouncil #ForbesTechCouncil #leadership #security #privacy #cloud #infosec #cybersecurity #AI #SaaS
@forbes @[email protected] @forbestechcncl @RHR_International @depaulu #DePaul #DepaulU #DePaulUniversity #DePaulCDM
Edited 142d ago
Breaking, new, by me: Iran-backed Hackers Claim Wiper Attack on Medtech Firm Stryker
A hacktivist group with links to Iran's intelligence agencies is claiming responsibility for a data-wiping attack against Stryker, a global medical technology company based in Michigan. News reports out of Ireland, Stryker's largest hub outside of the United States, said the company sent home more than 5,000 workers there today. Meanwhile, a voicemail message at Stryker's main U.S. headquarters says the company is currently experiencing a building emergency.
From the story:
"Wiper attacks usually involve malicious software designed to overwrite any existing data on infected devices. But a trusted source with knowledge of the attack who spoke on condition of anonymity told KrebsOnSecurity the perpetrators in this case appear to have used a Microsoft service called Microsoft Intune to issue a ‘remote wipe’ command against all connected devices."
"Intune is a cloud-based solution built for IT teams to enforce security and data compliance policies, and it provides a single, web-based administrative console to monitor and control devices regardless of location. The Intune connection is supported by this Reddit discussion on the Stryker outage, where several users who claimed to be Stryker employees said they were told to uninstall Intune urgently."
https://krebsonsecurity.com/2026/03/iran-backed-hackers-claim-wiper-attack-on-medtech-firm-stryker/

Computer maker #Framework notifies ‘all customers’ of a #DataBreach
https://techcrunch.com/2026/08/07/computer-maker-framework-notifies-all-customers-of-a-data-breach/
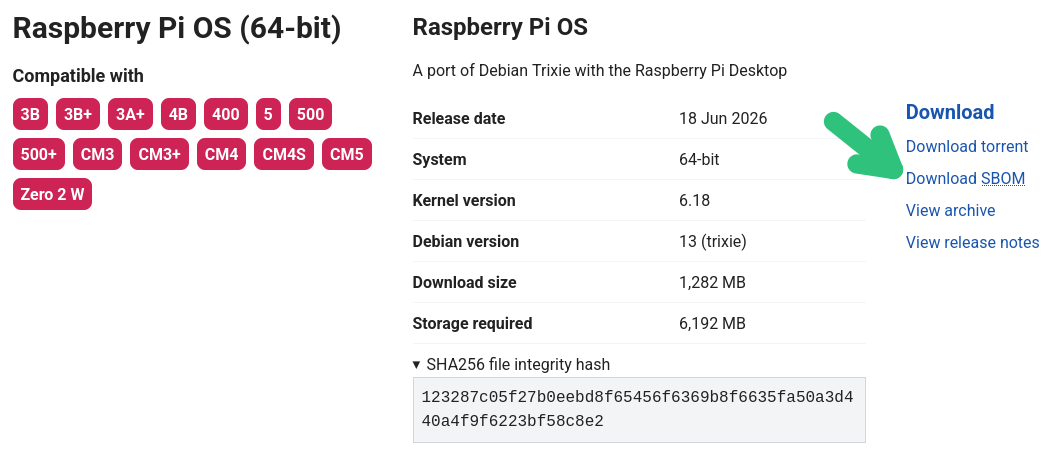
Raspberry Pi now publishes a Software Bill Of Materials (SBOM) with each PiOS download
and a torrent
and a link to the release notes
and a link to the release archive
and the release date
and a checksum
and the download and install storage sizes
and the architecture, kernel, and upstream release versions
and a list of all compatible hardware
in the same place.
https://www.raspberrypi.com/software/operating-systems/
How is your Enterprise software vendor doing?
#RaspberryPi #PiOS #SBOM #SoftwareBillOfMaterials #InfoSec #InformationSecurity #CyberSecurity
Edited 86d ago
Federal Cyber Experts Thought Microsoft’s Cloud Was “a Pile of Shit.” They Approved It Anyway.
---
A federal program created to protect the government against cyber threats authorized a sprawling Microsoft cloud product, despite the company’s inability to fully explain how it protects sensitive data.
https://www.propublica.org/article/microsoft-cloud-fedramp-cybersecurity-government?utm_source=mastodon&utm_medium=social&utm_campaign=mastodon-post
#News #Microsoft #Cybersecurity #Government #Technology #Tech #Cloud

I feel like there's a population of crypto and crypto-adjacent tech people who legitimately don't understand why a long, hard-to-guess string that is stored and shared in cleartext is very different from a password and cannot be substituted for one. I feel like a bunch of these folks don't understand why.
I'm not going to name and shame but I'm in the midst of a conversation on this, which is why it's top of mind.
#tech #dev #crypto #security #cybersecurity #InfoSec
I'm not going to name and shame but I'm in the midst of a conversation on this, which is why it's top of mind.
#tech #dev #crypto #security #cybersecurity #InfoSec
The US needs an information-warfare strategy for Iran — and beyond
The United States has demonstrated impressive combat power in the conflict with Iran. And yet, when Iranian authorities…
#EuropeSays #Headlines #News #Europe #Europa #EU #Iran #China #Cuba #cybersecurity #D2C #Global #informationwarfare #Myanmar #networks #OfficeofForeignAssetsControl #Op-EdCommentary #OpenTechnologyFund #OperationEpicFury #Russia #Starlink #StateDepartment #technology #VPN
https://www.europesays.com/iran/301257/
NEW: A Puerto Rico Government Agency Exposed 1 Million Social Security Numbers
A cybersecurity loophole in an official government mapping service left private data easily accessible, Centro de Periodismo Investigativo and ProPublica learned.
https://www.propublica.org/article/puerto-rico-crim-data-breach?utm_source=mastodon&utm_medium=social&utm_campaign=mastodon-post
#News #PuertoRico #Government #Cybersecurity #Data #Privacy #SocialSecurity #Tech #Technology
Watching the livestream of the Artemis II launch, I just witnessed one of the astronauts type in the password on their tablet while sitting in the capsule on camera.
#ArtemisII #Artemis #Artemis2 #NASA #InfoSec #cybersecurity #OpSec #Privacy #SpaceExploration
Edited 214d ago
NEW on “Paper Trail”: Reporter Renee Dudley heard Microsoft was running tech support for the Pentagon through China, the country’s biggest cybersecurity adversary.
She thought it sounded like a conspiracy theory — until she started looking into it.
Listen to the full episode: https://www.propublica.org/podcast/microsoft-digital-escorts-china-defense-department?utm_source=mastodon&utm_medium=social&utm_campaign=mastodon-post
#Podcast #Podcasts #Microsoft #Tech #Technology #Cybersecurity #Pentagon #Defense #China #Data #Journalism
What I’ve been reading (and watching) week ending 9 August https://jchyip.medium.com/what-ive-been-reading-and-watching-week-ending-9-august-1ab6b2dde859 #AI #DistributedSystems #science #engineering #SoftwareEngineering #cybersecurity #ProductManagement